Lesson 2 of 6 · about 55 minutes · Updated October 28, 2026
Client Data, E-Discovery, Cloud and AI Tools: Where Client Files Live and How to Keep Them Confidential
You'll be able to
- Map where client data lives in a law or accounting firm, including email, phones, backups, vendors and paper, and find the copies outside official systems.
- Classify client data into tiers (privileged, regulated personal and tax data, health information, trade secrets and protected material) and attach handling rules to each.
- Explain the federal e-discovery rules on proportionality, clawback, lost ESI and FRE 502, and how the Idaho civil and evidence rules differ.
- Describe legal holds, protective orders and HIPAA qualified protective orders, and when a firm becomes a HIPAA business associate.
- Evaluate cloud, e-discovery and generative AI vendors under Idaho Rule 5.3, ABA Opinions 08-451 and 512 and the AICPA Code, using due diligence questions and consumer versus enterprise terms.
- Apply Idaho Rule 1.16A, Rule 1.15(a), the FTC Disposal Rule and NIST SP 800-88 to returning, keeping and securely destroying client files.
Start here: the short version
- Client data in a law or accounting firm lives in far more places than the document management system: email, phones, file shares, cloud drives, e-discovery platforms, tax software, backups, vendors' systems and paper. You cannot protect what you have not mapped. Idaho Rule of Professional Conduct 1.6(c) requires "reasonable efforts" to prevent unauthorized access to all of it.1
- Not all client data is alike. Privileged communications, Social Security numbers, medical records from injury and malpractice cases, tax returns, trade secrets and sealed material each carry different rules, and the most sensitive class sets the controls for the whole matter file.
- In federal court, the 2015 rules added proportionality to discovery, a clawback procedure for privileged documents, and a narrower sanctions rule for lost electronic data, and Federal Rule of Evidence 502(d) lets a judge order that a privilege mistake is not a waiver.23 Idaho state court is different: Idaho Rule 26(b)(1) still uses the "reasonably calculated" test, Idaho Rule 37(e) keeps the older safe harbor, and no Idaho evidence rule matching FRE 502(b) or (d) was found.456
- Legal holds, protective orders and HIPAA qualified protective orders all say the same thing in different words: keep it, keep it locked, and give it back or destroy it when the case ends.7
- Every cloud service, review platform and IT company that touches client files is a nonlawyer assistant under Idaho Rule 5.3 (for CPAs, a third-party service provider under the AICPA Code). The firm stays responsible for what the vendor does.89
- ABA Formal Opinion 512 (July 29, 2024) says a lawyer needs the client's informed consent before putting client information into a self-learning generative AI tool, and that boilerplate in an engagement letter is not enough.10
- Idaho's own Rule 1.16A defines what is in the client file, lets lawyers keep it electronically, and bars destroying it while a claim, investigation or discipline matter is pending or expected.11
Rule versions described: Idaho Rules of Professional Conduct 1.1, 1.6, 1.9, 1.15, 1.16, 1.16A, 4.4 and 5.3 (Idaho State Bar text current as of March 9, 2026, read Oct 28, 2026); Federal Rules of Civil Procedure 26, 34 and 37 as amended effective December 1, 2015, and Federal Rule of Evidence 502 (Cornell LII text read Oct 28, 2026); Idaho Rules of Civil Procedure 26, 34 and 37 (adopted March 1, 2016, effective July 1, 2016) and Idaho Rules of Evidence 502 and 510 (effective July 1, 2018), read on isc.idaho.gov Oct 28, 2026; 45 CFR 160.103 and 164.512(e) (current eCFR text); ABA Formal Opinions 08-451 (2008), 477R (2017), 482 and 483 (2018), 498 (2021) and 512 (2024); 16 CFR 682.3 (FTC Disposal Rule) and 16 CFR 314.4 (FTC Safeguards Rule), current text read Oct 28, 2026; NIST SP 800-88 Revision 2 (September 2025). Rules and opinions change; check the current text from the court, bar or regulator before relying on any point.
A client hands a firm the most private parts of a life or a business: a divorce file with bank statements and text messages, a tax return with every dependent's Social Security number, a medical malpractice file with ten years of hospital records, the draft terms of a merger that would move a stock price, a trade secret the client spent a decade building. The firm's job is to use that information for the client and to keep everyone else away from it. The professional rules make that a duty, and the clients, courts and regulators are increasingly checking whether firms meet it.
This lesson is about where that information sits and how it travels. It covers mapping client data across a firm's systems, classifying it, handling it in discovery under both the federal and Idaho rules, legal holds and protective orders, securing review platforms and productions, choosing and supervising cloud and e-discovery vendors, using generative AI without giving client secrets away, and returning or destroying files when the work ends. It is written for law firms first, with the accounting and tax side covered where the rules differ.
The duties themselves (competence, confidentiality and supervision under Idaho Rules 1.1, 1.6 and 5.3) are explained in lesson 1, Competence, Confidentiality and Supervision. The general method for an asset and data inventory is in Risk Assessment and Data Mapping, and the basic settings for Microsoft 365, Google Workspace and shared links are in Cloud, SaaS and Shared Files. This lesson does not repeat those; it applies them to the client file.
Why client data is a target
Law and accounting firms sit where valuable information collects. A single firm may hold the deal documents of a dozen companies, the tax records of thousands of families and the medical files of hundreds of injured people. That concentration is the reason attackers bother with firms at all.
The clearest public example is a federal criminal case. In December 2016 the U.S. Attorney for the Southern District of New York announced charges against three men accused of using the stolen login credentials of law firm employees to reach firm servers, install malware and take partners' emails about pending mergers, then trade on the news. Prosecutors said at least seven firms were targeted, two were broken into, and the defendants made more than $4 million. The U.S. Attorney told law firms that "you are and will be targets of cyber hacking," because firms hold information valuable to criminals.12 The firms were not named in the charging papers.
The largest example of what happens when a firm's whole archive leaves the building is the 2016 Panama Papers. The International Consortium of Investigative Journalists reported about 11.5 million internal files, 2.6 terabytes, from the Panamanian firm Mossack Fonseca, covering more than 210,000 companies and records from 1977 through 2015.13 How the files left the firm was never officially established, and this lesson does not guess. The lesson for every firm is simpler: decades of client records were kept in one place that could be copied in bulk.
Firms also report gaps in basic controls. The ABA's 2023 Cybersecurity TechReport, based on its 2023 Legal Technology Survey, found that 29 percent of responding lawyers said their firm had experienced a security breach at some point, that file encryption was available to 48 percent and email encryption to 42 percent, and that only 34 percent had an incident response plan.14 Clients have noticed: 27 percent of respondents had been asked for the firm's security requirements, 22 percent had been asked to complete a security questionnaire, and 14 percent had a client request an audit or review.14
The rule that ties these facts to a duty is Idaho Rule of Professional Conduct 1.6(c): "A lawyer shall make reasonable efforts to prevent the inadvertent or unauthorized disclosure of, or unauthorized access to, information relating to the representation of a client."1 Idaho Comment [19] lists the factors for what is reasonable, starting with "the sensitivity of the information" and "the likelihood of disclosure if additional safeguards are not employed."1 Both factors depend on knowing what data the firm has and where it is. Idaho Rule 1.1 Comment [8] adds that lawyers should keep up with "the benefits and risks associated with relevant technology."15
Mapping where client data lives
ABA Formal Opinion 477R (2017) lists seven things a lawyer should do to secure client communications. The second is to "Understand How Client Confidential Information is Transmitted and Where It Is Stored."16 That is a data map. The ordinary method (inventory the systems, list the data in each, draw how it flows, then score the risks) is taught in Risk Assessment and Data Mapping. What follows is the professional firm version: the places client data actually turns up.
The places to look
| Location | What client data is there | The gap firms most often miss |
|---|---|---|
| Practice management system (law) or practice and workflow system (accounting) | Client names, contact details, matter descriptions, conflict data, time entries that describe the work, calendars, trust ledgers | Time entry narratives reveal privileged strategy; former staff accounts left active |
| Document management system | Drafts, final documents, client-provided records, work product | Everyone can open every matter; no "ethical wall" or need-to-know restriction on sensitive matters |
| Email and calendar | The bulk of client communication, attachments, forwarded records | Years of attachments never filed; auto-forwarding rules; personal accounts used "just this once" |
| File shares and local drives | Scans, spreadsheets, exhibits, downloaded productions | A "scans" or "temp" folder with thousands of unsorted client files and open permissions |
| Cloud storage and sharing links | Files sent to or received from clients, co-counsel, experts | Links that never expire and work for anyone who has them |
| Client portals | Uploaded tax documents, signed engagement letters, invoices | Portal accounts with no multi-factor sign-in; files never purged after the season or matter |
| E-discovery and review platforms | Whole mailboxes and file systems collected from clients and opponents | Contract reviewers keep access after the project; data stays hosted (and billed) for years |
| Tax and accounting software | Returns, W-2s, 1099s, bank and payroll data, prior years | Desktop installs with local databases on unencrypted laptops; e-file credentials shared |
| Phones and tablets | Texts with clients, photos of documents, email copies, messaging apps | Personal phones with no screen lock policy or remote wipe; client texts that are not preserved |
| Backups | Copies of everything above, often going back years | Backups kept longer than the retention schedule allows, unencrypted, and out of reach of holds and destruction |
| Vendors | Court reporters, experts, translators, copy and scan shops, payroll and bill pay, IT providers | No list of which vendor holds which client's data |
| Paper | Original wills and deeds, intake forms, medical records, bankers boxes in storage | Off-site storage with no inventory; recycling bins instead of shredding |

Building the map in a week
A small firm does not need consultants to produce a useful first map. It needs one person with authority, a spreadsheet and a week of interviews.
- Pick two or three real matters of different types (for example a personal injury case, an estate plan and a business sale, or for a CPA firm an individual return, a payroll client and an audit). Following real files finds more than asking about systems in the abstract.
- For each matter, trace every place a piece of client information went: who received it, how (portal, email, mail, text), where it was saved, who it was sent to, and where copies remain. Include the paralegal's desktop, the expert's email and the copy shop.
- List each system and vendor that turned up, with the owner inside the firm, who has access, whether multi-factor sign-in is on, whether the data is encrypted at rest, and how long it is kept.
- Mark which classes of data (see the next section) each location holds. A location that holds health records or Social Security numbers gets stricter controls than one that holds only names.
- Note every place the data is kept longer than the firm's retention schedule says, and every place the firm cannot reach to apply a legal hold or destroy a file. Those are the gaps to fix first.
- Repeat when the firm adds a major system, changes IT providers, opens a new practice area or merges.
The copies nobody counts
Interviews nearly always turn up copies outside the official systems. The common ones are attachments saved to a desktop "to work on at home," productions downloaded from a review platform to a laptop for a deposition, client texts on a lawyer's personal phone, files synced to a personal cloud account by a desktop app, scanned intake packets left in a multifunction copier's memory, and exports created for an expert or a mediator that no one deleted. Each copy is covered by Rule 1.6(c) just as fully as the original. For accounting firms the classic stray copy is the prior year's tax database on an old laptop that was never wiped.
Two places deserve special mention. The first is backups. A firm that carefully destroys a closed file on its live systems may still hold it for years in backups, where it can be stolen in a ransomware attack or swept into a later subpoena. The second is time entries. Narratives such as "call with client re: possible fraud by CFO" are client confidences and, in many cases, privileged. They sit in the billing system and on invoices, and they are often less protected than the documents they describe.
Classifying client data
ABA Opinion 477R's fifth consideration is "Label Client Confidential Information."16 Classification is how a firm decides which files get which protection. Every piece of client information is confidential under Rule 1.6(a), which covers all "information relating to the representation of a client," not just secrets or privileged material.1 But inside that broad category, some data carries extra legal rules, and a firm that treats a medical chart the same as a newsletter list is either overspending on the newsletter or underprotecting the chart.
Privileged communications and work product
Attorney-client privilege and work-product protection are evidence and procedure rules, separate from the ethics duty of confidentiality. They protect a narrower set of material (communications for legal advice, and documents prepared in anticipation of litigation), but losing them can be permanent. In Idaho state court, Idaho Rule of Evidence 510 says the privilege is waived if the holder "voluntarily discloses or consents to disclosure of any significant part of the matter or communication."6 A misdirected email or a sloppy production can put the privilege at risk, which is why the clawback rules discussed below matter so much.
Accountants have a narrower Idaho rule of their own. Idaho Code 9-203A says a licensed public accountant or CPA "cannot, without the consent of his client, be examined as a witness as to any communication made by the client to him, or his advice given thereon in the course of professional employment," with exceptions for Board of Accountancy proceedings and quality review.17
Personal information under Idaho breach law
Idaho's breach notice statute protects a narrow list: an Idaho resident's first name or first initial and last name together with a Social Security number, a driver's license or Idaho ID card number, or a financial account or card number with the code needed to access the account, when the name or the numbers are not encrypted.18 Law and accounting files are full of these combinations: intake forms, settlement statements, W-2s, bank statements, loan files. A firm that holds this data for a client it represents (rather than owning it) must "give notice to and cooperate with the owner or licensee of the information of any breach" immediately after discovery when misuse has occurred or is reasonably likely.18 Notice duties are covered in lesson 5, Engagement Letters, Incident Response and Notice.
Health information from injury and malpractice cases
Personal injury, medical malpractice, workers' compensation, Social Security disability, guardianship and employment cases all bring medical records into the firm. Idaho Rule 1.16A even lists "medical records" among the materials that make up the client file.11 Who sent the records matters. Records the client brings in or authorizes are protected by Rule 1.6. Records a firm receives from a hospital or doctor client, or obtains under a subpoena with a qualified protective order, bring HIPAA's rules along with them (see the section on protective orders below). Idaho's breach statute does not list medical information at all, so for a firm the protection for health records comes from the professional rules, from HIPAA when it applies, and from court orders.18
Financial and tax records
Tax returns and the documents behind them are the core of an accounting firm and turn up constantly in law firms (divorce, estate, business disputes). For a tax preparer, return information has its own federal rules: 26 U.S.C. 7216 makes knowing or reckless unauthorized disclosure a crime, and the regulations at 26 CFR 301.7216 require a specific written client consent before most uses or disclosures, including before return information is disclosed to a preparer outside the United States.19 The FTC Safeguards Rule names "an accountant or other tax preparation service that is in the business of completing income tax returns" as a financial institution and requires encryption of customer information "both in transit over external networks and at rest."20 Those rules are the subject of lesson 4, Accounting and Tax Firms: GLBA Safeguards and IRS Rules.
Trade secrets, deal data and sealed or protected material
ABA Opinion 477R singles out "industrial designs, mergers and acquisitions or trade secrets, and industries like healthcare, banking, defense or education" as matters that may call for more than ordinary security.16 The Southern District of New York case described above shows why: pending merger information is worth money to anyone who reads it first.12 Material produced under a protective order, filed under seal or designated "attorneys' eyes only" adds a court order on top of the ethics rule. Violating the order is a separate problem from a confidentiality lapse, and the order itself usually says who may see the material, where it may be stored and what happens to it at the end of the case.
A classification scheme only works if it changes behavior. Keep it short (three or four tiers), attach each tier to a few concrete handling rules, and set it at the matter level rather than asking staff to label every document. A matter that contains any restricted material is handled as restricted. Idaho Comment [19] also notes that a client "may require the lawyer to implement special security measures not required by this Rule or may give informed consent to forgo security measures that would otherwise be required."1 Record those client instructions on the matter, where staff will see them.
E-discovery under the federal rules
Electronic discovery, usually shortened to e-discovery, is the process of preserving, collecting, reviewing and producing electronically stored information (ESI) in litigation. It is also the moment when a firm moves the largest amount of other people's data: whole mailboxes from the client, productions from the other side, and copies for experts and vendors. The federal rules that govern it were rewritten effective December 1, 2015.2
Proportionality: Rule 26(b)(1)
Federal Rule of Civil Procedure 26(b)(1) allows discovery of "any nonprivileged matter that is relevant to any party's claim or defense and proportional to the needs of the case," considering "the importance of the issues at stake in the action, the amount in controversy, the parties' relative access to relevant information, the parties' resources, the importance of the discovery in resolving the issues, and whether the burden or expense of the proposed discovery outweighs its likely benefit."2 The 2015 amendment removed the old phrase allowing discovery "reasonably calculated to lead to the discovery of admissible evidence."
Proportionality is usually argued as a cost issue, but it is also a security tool. Every extra custodian, date range and data source collected is more data the firm and its vendors must protect. Narrow, well-negotiated collections mean fewer copies of sensitive data in the world.
The Rule 26(f) conference and the ESI plan
Rule 26(f)(3) requires the parties' discovery plan to address "any issues about disclosure, discovery, or preservation of electronically stored information, including the form or forms in which it should be produced," and privilege issues, including whether to ask for "an order under Federal Rule of Evidence 502."2 That conference is the place to settle security terms before data moves: how productions will be transferred and encrypted, who on each side may see confidential material, whether a protective order with data security terms will be proposed, and what happens to the data at the end.
Form of production: Rule 34
Under Rule 34(b)(2)(E)(ii), if no form is specified, ESI must be produced "in a form or forms in which it is ordinarily maintained or in a reasonably usable form or forms."21 Native files (the original spreadsheet or email file) carry metadata such as authors, edit history, hidden rows and comments. Image formats (TIFF or PDF with extracted text) carry less. The choice affects both what the other side learns and what the producing firm must check before it sends anything. Hidden spreadsheet tabs and tracked changes have exposed privileged notes in productions; the production hygiene section below covers the checks.
Clawback: Rule 26(b)(5)(B) and Federal Rule of Evidence 502
Large productions produce mistakes. Rule 26(b)(5)(B) sets the clawback procedure: after the producing party gives notice of a privilege claim, the receiving party "must promptly return, sequester, or destroy the specified information and any copies it has; must not use or disclose the information until the claim is resolved."2 The rule is a procedure, not a decision on whether the privilege survived.
Federal Rule of Evidence 502 answers that question. Under 502(b), an inadvertent disclosure in a federal proceeding is not a waiver if "(1) the disclosure is inadvertent; (2) the holder of the privilege or protection took reasonable steps to prevent disclosure; and (3) the holder promptly took reasonable steps to rectify the error."3 Under 502(d), "A federal court may order that the privilege or protection is not waived by disclosure connected with the litigation pending before the court," and the order then binds "any other federal or state proceeding."3
The practical difference is large. Under 502(b), a firm that made a mistake must prove its precautions were reasonable, which invites the other side to probe the firm's review process. A 502(d) order removes that fight. Many litigators ask for one at the Rule 26(f) conference as a matter of routine, and the rule's text invites them to.
The receiving side has duties too. Idaho Rule of Professional Conduct 4.4(b) requires a lawyer who receives a document or ESI and "knows or reasonably should know that the document or electronically stored information was inadvertently sent" to "promptly notify the sender." Idaho Comment [4] says this includes metadata only when the receiving lawyer knows or reasonably should know it was sent by mistake, and leaves return, deletion and waiver to other law.22 ABA Formal Opinion 06-442 found no Model Rule bar on reviewing metadata and pointed senders to scrubbing metadata from documents before sending them.23
Lost electronic information: Rule 37(e)
Federal Rule 37(e), as amended in 2015, applies when ESI "that should have been preserved in the anticipation or conduct of litigation is lost because a party failed to take reasonable steps to preserve it, and it cannot be restored or replaced through additional discovery." If the loss prejudices another party, the court "may order measures no greater than necessary to cure the prejudice." Only if the court finds the party "acted with the intent to deprive another party of the information's use in the litigation" may it presume the information was unfavorable, give an adverse-inference instruction, or dismiss the case or enter a default judgment.24
Two security points follow. First, "reasonable steps to preserve" includes protecting preserved data from loss: a hold that sits on a server that gets encrypted by ransomware, with no clean backup, is a preservation failure waiting to be explained. Second, the intent requirement for the harshest sanctions does not make careless loss safe; cure measures can still be expensive.
Idaho state court is different
Idaho rewrote its civil rules in 2016 (adopted March 1, effective July 1, 2016), but it did not copy every 2015 federal change.4 A firm that litigates in both systems needs to know where they part ways, because the security planning for a case depends on the rules that govern it.
| Topic | Federal court | Idaho state court | Why it matters for data handling |
|---|---|---|---|
| Scope of discovery | FRCP 26(b)(1): relevant and "proportional to the needs of the case" (2015) | I.R.C.P. 26(b)(1)(A): relevant to any party's claim or defense; relevant information need not be admissible "if the discovery appears reasonably calculated to lead to the discovery of admissible evidence"; no federal-style proportionality factors in the text | Broader requests are easier to justify in state court, so more data may be collected and held. Narrow by agreement where you can. |
| Hard-to-reach ESI | FRCP 26(b)(2)(B): sources not reasonably accessible | I.R.C.P. 26(b)(1)(B): similar limit for sources "not reasonably accessible because of undue burden or cost" | Backups and legacy systems may be off the table unless the court finds good cause. Document why a source is inaccessible. |
| Clawback procedure | FRCP 26(b)(5)(B) | I.R.C.P. 26(b)(5)(B): parallel procedure (return, sequester or destroy; no use until resolved) | The procedure exists in both. It does not decide waiver. |
| Discovery planning conference | FRCP 26(f) requires an ESI and privilege plan | No Rule 26(f) counterpart appears in the text of I.R.C.P. 26 read for this lesson | Security terms must be raised by agreement or motion rather than through a required conference. |
| Form of production | FRCP 34(b)(2)(E): ordinary or reasonably usable form | I.R.C.P. 34(b): same standard, plus the court may order the requesting party to pay for "extraordinary steps" | Cost shifting can encourage narrower requests. |
| Lost ESI sanctions | FRCP 37(e) (2015): cure measures; harshest sanctions only on intent to deprive | I.R.C.P. 37(e): the older safe harbor for ESI "lost as a result of the routine, good-faith operation of an electronic information system," plus a general sanctions power in 37(f) | Routine deletion is protected only if it is truly routine and in good faith. Suspend it once a hold applies. |
| Privilege waiver protection | FRE 502(b) (inadvertent disclosure) and 502(d) (court order binding other proceedings) | I.R.E. 502 is the lawyer-client privilege itself; I.R.E. 510 makes voluntary disclosure of "any significant part" a waiver. No equivalent of FRE 502(b) or (d) was found | In state court, protect privilege with a stipulated clawback agreement and a protective order, and review productions carefully. |
The Idaho text quoted in the table is from the rules as posted by the Idaho Supreme Court, read October 28, 2026.42556 The conclusion that Idaho has no FRE 502(b) or (d) equivalent comes from reading the Idaho evidence rules, not from a court decision on the point. A federal 502(d) order does reach state proceedings, by its own terms, when the disclosure happened in the federal case.3 When a case is in Idaho state court from the start, the parties' own written agreement and a court-entered protective order are the main tools. Idaho Rule 26(c)(1)(G) lets the court order "that a trade secret or other confidential research, development, or commercial information not be revealed or be revealed only in a specified way."4
What the differences mean for security
Three practical points follow for Idaho practitioners. First, because state court discovery can reach further, expect to receive, host and protect larger volumes of the other side's data, and budget for it. Second, because the privilege protection is thinner, the review before production matters more: a privilege search, a second-level check of anything that hits on privileged names, and a metadata and hidden-content scrub before release. Third, because Idaho's 37(e) protects "routine, good-faith" loss, a firm whose client's systems auto-delete email after 90 days must make sure the auto-delete is switched off for the right custodians once a duty to preserve arises. Routine deletion that continues after the duty arises is hard to call good faith.
Legal holds
A legal hold (also called a litigation hold or preservation notice) is the instruction to stop deleting information that may be relevant to a dispute. The general method for running holds in any business, including triggers, owners and a sample notice, is taught in Records Retention, Legal Holds and Workplace Privacy. This section covers what is different when the business is a law or accounting firm.
Zubulake and the duty to preserve
The most cited case on holds is Zubulake v. UBS Warburg LLC, 220 F.R.D. 212 (S.D.N.Y. 2003), known as Zubulake IV, decided by Judge Shira Scheindlin on October 22, 2003.26 In an employment discrimination case where the employer had lost some backup tapes and emails, the court held that once a party reasonably anticipates litigation, it must set aside its routine retention and destruction practices and put a litigation hold in place for relevant documents. The opinion described whose documents had to be kept (the "key players") and discussed how backup tapes fit into the duty. Zubulake IV predates the 2015 federal rule changes, and the sanctions framework it applied has since been replaced by Rule 37(e) in federal court, but its basic description of when the duty begins and what a hold must reach is still taught everywhere.
Two kinds of holds in a firm
A firm deals with holds in two roles, and they are easy to confuse.
- Holds the firm manages for a client. In litigation, the lawyer advises the client to issue a hold, helps identify custodians and systems, and often hires the e-discovery vendor that collects the data. The data then sits in the client's systems, the vendor's platform and the firm's review database at the same time.
- Holds on the firm's own records. A firm can be a party too: a malpractice claim, a fee dispute, an employment case, a disciplinary investigation, or a subpoena for records about a client. Idaho Rule 1.16A(g) makes this concrete for client files: a lawyer "shall not destroy a client's file" if the lawyer knows or reasonably should know that a related lawsuit or claim, a criminal or governmental investigation, or "a disciplinary investigation or proceeding related to the client's matter or a Client Assistance Fund claim is pending or anticipated."11
Where holds and security collide
Holds and good security practice pull in opposite directions. Security says keep less: delete old data, shorten retention, purge closed files. Holds say keep everything that might matter. A firm needs a process that does both.
- Auto-delete and retention policies. Email retention rules, Teams or Slack message expiry, and phone settings that delete texts after 30 days all keep running until someone turns them off for the custodians on hold. Use the platform's built-in hold feature where it exists, rather than telling people not to delete.
- Messaging apps. Client texts and messaging apps on personal phones are a frequent preservation failure. If a lawyer or client discusses the matter by text, those messages are ESI and may need to be preserved.
- Ransomware and recovery. Restoring from a backup after an attack can roll mailboxes back to a date before held data was created, and wiping infected machines can destroy held data. Incident response plans should include a step to check active holds before restoring or wiping. ABA Formal Opinion 482 on disasters says that "proper advance preparation and planning" reduces the risk of violating the rules after a disaster.27
- Departing staff. When an employee on hold leaves, their mailbox and laptop must be preserved, not recycled on the usual schedule.
- Releasing holds. Held data should go back to the normal retention schedule when the matter ends. A firm that never releases holds ends up keeping everything forever, which is a security problem of its own.
Protective orders and HIPAA qualified protective orders
Ordinary protective orders
A protective order is a court order that limits how discovery material may be used and who may see it. Under both the federal and Idaho versions of Rule 26(c), a court may, for good cause, limit disclosure, set terms, designate who may be present, and require that a trade secret or other confidential commercial information "not be revealed or be revealed only in a specified way."4 Stipulated protective orders usually create tiers ("confidential" and "highly confidential, attorneys' eyes only") and list who may see each tier: the lawyers, their staff, retained experts who sign an acknowledgment, the court and its staff, court reporters and vendors.
Most model protective orders say little about information security. Firms that represent clients with sensitive data increasingly propose added terms: storage only on systems with access controls and multi-factor sign-in, encrypted transfer, a duty to notify the producing party of a breach involving its material within a set number of days, a ban on uploading designated material to public AI tools, and certification of return or destruction at the end. A firm should be able to meet the terms it proposes, so check with the firm's IT lead before offering them.
HIPAA qualified protective orders
When a party seeks medical records from a hospital or doctor by subpoena or discovery request without a court order, HIPAA lets the provider disclose them only if it receives "satisfactory assurance" either that the patient was given notice and a chance to object, or that the requesting party has made reasonable efforts to secure a qualified protective order.7 Under 45 CFR 164.512(e)(1)(v), a qualified protective order is a court order or a stipulation that:
"(A) Prohibits the parties from using or disclosing the protected health information for any purpose other than the litigation or proceeding for which such information was requested; and (B) Requires the return to the covered entity or destruction of the protected health information (including all copies made) at the end of the litigation or proceeding."7
Two words in that text drive firm practice: "all copies." A malpractice file may have medical records on the review platform, in the expert's email, in deposition exhibit sets, in the trial notebook, in the paralegal's downloads folder and in backups. A firm that signs a qualified protective order needs a way to find and destroy every one of those copies at the end of the case, and to document it. The data map from earlier in this lesson is how.
When the firm is a business associate
A different HIPAA rule applies when a firm's client is the health care provider or health plan. HIPAA's definition of a business associate, in 45 CFR 160.103, includes a person who provides "legal, actuarial, accounting, consulting, data aggregation ... management, administrative, accreditation, or financial services" to a covered entity, "where the provision of the service involves the disclosure of protected health information."28 A firm defending a hospital in a malpractice case, auditing a clinic's books or advising a health plan is usually a business associate, which means a business associate agreement, HIPAA Security Rule safeguards for the electronic health information it holds, and breach notice duties to the client.
New York's Attorney General showed what that looks like in practice. In March 2023 the office announced a $200,000 settlement with Heidell, Pittoni, Murphy & Bach LLP, a firm that represents New York City area hospitals. According to the Attorney General, an attacker exploited a Microsoft Exchange vulnerability for which "Patches for this vulnerability had been released by Microsoft several months earlier"; the firm later found that "tens of thousands of files had been potentially taken," exposing data of about 114,979 people, including Social Security numbers and medical information. The office cited HIPAA and required the firm to adopt a written information security program with encryption, logging and monitoring, patch management, penetration testing and data minimization.29
Business associate duties are taught in full in Healthcare Cybersecurity and HIPAA, lesson 6: Business Associates, Cloud and AI Vendors, and HIPAA basics are in Health Privacy: HIPAA and Beyond. The point for this lesson is that a firm with health care clients should flag those matters in its data map, because their records carry contract and federal duties on top of Rule 1.6.
The Sedona Conference
The Sedona Conference is a nonprofit research and educational institute whose working groups of judges, practitioners and technologists publish commentary on electronic discovery, privacy and data security. Its best-known work, The Sedona Principles, Third Edition: Best Practices, Recommendations and Principles for Addressing Electronic Document Production, was published in 2018 in The Sedona Conference Journal, volume 19, number 1, and contains 14 principles.30 One principle (Principle 6) says that responding parties are best situated to evaluate the procedures for preserving and producing their own ESI. Federal courts cite Sedona publications often; the Eastern District of Pennsylvania posts a copy of the Principles on its website.30
The Sedona publications are commentary, not law. Courts treat them as persuasive descriptions of good practice, which makes them useful for a firm writing its own procedures: a hold or production process that tracks Sedona's recommendations is easier to defend as "reasonable." The Principles are free to download, though some Sedona materials require registration. This lesson describes them rather than quoting them at length; read the current text before relying on any particular principle.
Securing review platforms and productions
Most firms do not run their own e-discovery software. They hire a vendor that hosts a review platform, or they license a cloud tool. Either way, the platform may hold more sensitive data than anything else the firm touches: the entire mailbox of a client's chief executive, the other side's trade secrets, and thousands of medical records. The controls below are the ones to check.
Encrypted transfer
Data moves into a review platform from the client or a forensic collector, and productions move out to the other side. ABA Opinion 477R says that for sensitive information "a lawyer should encrypt the transmission," and mentions the use of "a well vetted and secure third-party cloud based file storage system."16 In practice that means a secure file transfer site or the platform's own encrypted delivery, not email attachments, and encrypted drives (with the password sent by a separate channel) when physical media must be shipped. Keep a record of every transfer: what was sent, to whom, when, how, and the Bates range. That log is what lets a firm answer quickly if a production is intercepted or misdirected.
File transfer tools are themselves a target. In May and June 2023 the Cl0p criminal group exploited an unknown flaw in Progress Software's MOVEit Transfer product, a tool many organizations used for exactly this kind of secure delivery. Press reports, citing RollOnFriday, named Kirkland & Ellis, K&L Gates and Proskauer Rose among the law firms affected, and Law.com reported a class action filed against Kirkland in June 2024 over the incident.31 A firm cannot patch a vendor's product, but it can ask whether its vendors use such tools, how fast they patch, how long files stay on the transfer server (MOVEit-style servers that keep files for months expose far more than ones that purge after download), and whether the vendor will tell the firm promptly when a flaw is announced.
Access lists
Review platforms are often used by large, changing teams: associates, paralegals, contract reviewers hired for a few weeks, co-counsel, experts and the vendor's own project managers. Set access by matter and by role, require multi-factor sign-in for every user, turn off bulk download and printing for reviewers who do not need it, and review the user list at least monthly and at every staffing change. Contract reviewers should lose access the day their engagement ends. ABA Formal Opinion 498 on virtual practice lists "multi-factor authentication to access firm systems" among the tools lawyers should consider.32 The platform's audit log, which records who viewed or exported what, should be kept for the life of the matter so the firm can investigate if a document turns up where it should not.
Vendor certifications, described
Vendors usually answer security questions by pointing to an independent report or certification. The most common in the United States is a SOC 2 report, an examination by a CPA firm using the AICPA's Trust Services Criteria, which cover five categories: security, availability, processing integrity, confidentiality and privacy.33 A Type 1 report looks at whether controls were designed properly at a point in time; a Type 2 report tests whether they worked over a period, usually six to twelve months, and is the more useful one. Read the report's scope (which services and data centers it covers), the list of exceptions the auditor found, and the "complementary user entity controls," which are the things the vendor expects the firm itself to do, such as managing its own user accounts. Another common credential is ISO/IEC 27001 certification, which shows the vendor runs a managed information security program audited against an international standard; ask for the certificate and its scope. Neither report proves a vendor will never be breached, and a vendor's marketing summary is not the report. How to read a SOC 2 report in more depth is covered in Vendors, Contracts and Third-Party Risk.
Production hygiene
Before anything leaves the firm, check four things:
- Privilege. Run privilege searches (lawyer names, firm domains, words such as "privileged" and "legal advice"), have a second reviewer check every document that hits, and log what is withheld in a privilege log as the rules require.
- Hidden content and metadata. Hidden rows and sheets, comments, tracked changes, speaker notes and embedded objects travel with native files. Decide deliberately whether to produce natively or as images, and scrub what should not go. ABA Opinion 06-442 points to scrubbing metadata, or sending a version without the embedded information, as the sender's protection.23
- Redaction. Redactions must remove the underlying text, not just draw a black box over it. Test a sample of redacted files by copying the text out of them before production.
- Personal identifiers. Even when a document is responsive, Social Security numbers, account numbers and similar identifiers of non-parties can often be redacted by agreement. Court filing rules separately require redaction of certain identifiers in public filings; check the court's current rule.
Return or destruction at matter end
A review database that stays hosted after a case ends keeps costing money and keeps the risk alive. At the close of each matter, the firm should decide, matter by matter, what to keep in the client file under its retention rules, what the protective order or qualified protective order requires to be returned or destroyed, and what the vendor must delete. Get a written certificate of destruction from the vendor, from experts and consultants, and from the other side where the protective order requires one. Then confirm the matter is closed on the vendor's invoice. The retention section later in this lesson covers the firm's own file.
Vendors and cloud services
Idaho Rule 5.3 and ABA Opinion 08-451
Idaho Rule of Professional Conduct 5.3 requires partners and managers to make "reasonable efforts to ensure that the firm has in effect measures giving reasonable assurance" that a nonlawyer's "conduct is compatible with the professional obligations of the lawyer."8 Idaho Comment [3], identical to the ABA comment, names the exact vendors this lesson is about. Its examples of nonlawyers outside the firm include "hiring a document management company to create and maintain a database for complex litigation, sending client documents to a third party for printing or scanning, and using an Internet-based service to store client information."8 The comment says the right level of effort depends on factors including "the terms of any arrangements concerning the protection of client information; and the legal and ethical environments of the jurisdictions in which the services will be performed, particularly with regard to confidentiality."8
ABA Formal Opinion 08-451 (August 5, 2008), on outsourcing, says a lawyer may outsource legal or nonlegal support services as long as the lawyer stays responsible for competent representation under Model Rule 1.1. It calls for disclosure to the client and client consent when outside providers "will be receiving information protected by Rule 1.6," and at a minimum suggests "reference checks and investigating the background" of the provider.34 Much earlier, ABA Formal Opinion 95-398 (1995) said that a lawyer who lets a computer maintenance company reach client files "must make reasonable efforts to ensure that the company has in place, or will establish, reasonable procedures to protect the confidentiality of client information."35 Today's IT provider with remote access to every server is the same problem on a larger scale.
Idaho has no State Bar ethics opinion on cloud computing. The Idaho State Bar's ethics committee stopped issuing formal opinions in the 1990s; the list on its website runs to No. 136 (1999), with a newer No. 137 in 2024 on the public defender transition, and none addresses cloud storage, email encryption or data breaches.36 Idaho lawyers therefore work from the rule comments and the ABA opinions.
Disasters, ransomware and Opinion 482
ABA Formal Opinion 482 (September 19, 2018) addresses floods, fires and other disasters, but its reasoning fits ransomware and vendor outages. It says Rule 1.1 "requires lawyers to develop sufficient competence in technology to meet their obligations under the Rules after a disaster" and that Rule 1.15 "requires lawyers to protect trust accounts, documents, and property the lawyer is holding for clients or third parties."27 For data that means backups the firm has actually restored from in a test, copies held somewhere a single attack or outage cannot reach, and a written plan for how the firm keeps working and reaches clients if its practice management or document system is unavailable for days. Ask each cloud vendor what happens to the firm's data if the vendor goes out of business, is acquired or suffers its own ransomware attack, and how the firm gets a complete export.
Virtual practice and Opinion 498
ABA Formal Opinion 498 (March 10, 2021) confirms that the Model Rules "permit virtual practice" and asks lawyers to review the terms of service of the hardware and software they use, secure video meetings, and handle documents and mail securely when working from home. It adds a practical point about home offices: unless a smart speaker or virtual assistant is helping with the practice, "the lawyer should disable the listening capability of devices or services such as smart speakers, virtual assistants, and other listening-enabled devices while communicating about client matters."32 Home printers, shared family computers and personal cloud sync apps are part of the data map for any lawyer or accountant who works remotely.
The accounting and tax side
CPAs have parallel rules. The AICPA Code's interpretation on disclosing information to a third-party service provider (ET 1.700.040) says that before disclosing confidential client information to a service provider, a member should either have a contract requiring the provider to keep it confidential with "reasonable assurance" of appropriate procedures, or obtain the client's specific consent. A companion interpretation (ET 1.150.040) says the member should tell the client, "preferably in writing," that a third-party provider may be used, though no notice is needed for administrative support such as record storage or software hosting.9 Idaho's accountancy rules incorporate the AICPA standards by reference.37 For tax return information, 26 CFR 301.7216 adds that disclosure to a preparer located outside the United States requires the taxpayer's prior written consent.19 And the FTC Safeguards Rule requires covered firms to select service providers capable of protecting customer information, require safeguards by contract, and periodically assess them.20 Lesson 4 covers these rules in detail.
Due diligence questions for cloud and e-discovery vendors
Questions are only useful if someone reads the answers and the firm is prepared to walk away. Ask these before signing, keep the answers in the vendor file, and ask again at renewal.
| Question | Why it matters | A good answer looks like |
|---|---|---|
| Do you have a current SOC 2 Type 2 report or ISO/IEC 27001 certificate covering the service we will use? May we read it? | Independent evidence beats a questionnaire | A report dated within the last 12 months, covering the right product and data centers, with exceptions explained |
| Is our data encrypted at rest and in transit? Who holds the keys? | Rule 1.6(c); 477R; Safeguards Rule 314.4(c)(3) for tax firms | Encryption by default; vendor staff access to plain data limited and logged |
| Is multi-factor sign-in required for all users, including your administrators? | Stolen credentials are a leading way in; the 2016 law firm hacking case began with them | Required, not optional; phishing-resistant options available |
| Where is our data stored and processed, and which subcontractors can reach it? | Idaho Rule 5.3 Comment [3] (jurisdictions); 7216 offshore consent for tax data | Named countries and subcontractors; notice before changes |
| Do you use our data to train AI models or for any purpose besides serving us? | ABA Op. 512 informed consent; Rule 1.6 | No, in the contract, not only in a policy page that can change |
| How fast will you notify us of a security incident involving our data? | The firm's own notice duties to clients (Op. 483; Idaho Code 28-51-105) | A fixed number of hours or days in the contract, with a named contact |
| Can we get a complete export in a usable format, at any time, and at the end? | Op. 482 continuity; client file duties under Rule 1.16A | Yes, documented, without a punitive fee |
| What happens to our data at termination, and will you certify deletion, including backups? | Qualified protective orders and protective orders require return or destruction | Deletion within a stated time, backups aged out on a stated schedule, written certificate |
| Will you sign a business associate agreement if we send PHI? | 45 CFR 160.103; firms with health care clients | Yes, with subcontractor agreements down the chain |
| Do you carry cyber insurance, and what limits? | A vendor without resources cannot pay for a breach it causes | Limits that match the volume of data held |
| How will you respond to a subpoena or government request for our data? | Privilege and confidentiality | Notice to the firm before responding, unless legally barred |

For smaller firms the honest answer is that big cloud vendors will not negotiate their contracts. That does not end the duty. The firm can still read the standard terms and the SOC 2 report, choose the business tier of a service rather than the consumer tier, turn on the security settings the vendor offers, and document why it chose that vendor. That record is what shows "reasonable efforts" under Rule 1.6(c) and Rule 5.3. The basic settings for common cloud suites are in Cloud, SaaS and Shared Files.
Generative AI tools
Generative AI tools (chat assistants, drafting tools, document summarizers and review tools that write or analyze text) arrived in law and accounting offices quickly, often through staff using free consumer accounts before the firm had a policy. The confidentiality question is simple to state: when someone pastes a client's facts into a tool, where does that text go, who can read it, and can it come back out in someone else's answer?
What ABA Formal Opinion 512 says
ABA Formal Opinion 512, "Generative Artificial Intelligence Tools," issued July 29, 2024, is the ABA's main guidance. It applies existing rules rather than creating new ones, and it touches seven duties: competence, confidentiality, communication, supervision, meritorious claims, candor to the court, and reasonable fees.10 The parts that bear on data handling:
- Competence (Rule 1.1). Lawyers must understand the tools they use well enough to judge their output. The opinion warns that "uncritical reliance on content created by a GAI tool can result in inaccurate legal advice to clients or misleading representations to courts," and notes the tools can produce "hallucinations."10
- Confidentiality (Rule 1.6). Before entering client information into a "self-learning" tool, one that may use inputs to train or improve itself so that the information could surface for other users, the lawyer needs the client's informed consent. The opinion says "merely adding general, boiler-plate provisions to engagement letters purporting to authorize the lawyer to use GAI is not sufficient."10 The risk also runs inside the firm: a tool shared across the firm could reveal one client's information to lawyers working for another.
- Reading the terms. "As a baseline, all lawyers should read and understand the Terms of Use, privacy policy, and related contractual terms and policies of any GAI tool they use," or rely on someone who has, such as IT or cybersecurity professionals.10
- Communication (Rule 1.4). Some uses must be disclosed to the client, for example when the use affects the representation or the client asks.
- Supervision (Rules 5.1 and 5.3). Managers must set clear policies on permitted tools and train lawyers and staff, and the vendors behind AI tools are outside nonlawyers whose services must fit the lawyer's duties.
- Fees (Rule 1.5). Lawyers billing hourly "must bill for their actual time," and a tool that works like general office software is overhead, not a separate charge, unless disclosed in advance.10
Idaho has not issued its own AI ethics opinion; as noted above, the Idaho State Bar has not issued technology opinions at all, so Idaho lawyers look to Rules 1.1, 1.6 and 5.3 and to Opinion 512.36 CPAs face the same practical issue under the AICPA confidentiality rule and, for return information, the 7216 consent rules: putting a client's return data into an outside AI service is a disclosure to a third party.919
Consumer versus enterprise terms
The single most useful fact about AI tools for confidentiality is that the same company often offers very different data terms for consumer and business accounts. OpenAI is a good example because it states both sides publicly. Its help page on model training says that for its consumer services (the free and paid individual ChatGPT plans), "we may use your content to train our models," and that users can opt out through a "Data controls" setting. The same page says it does not use inputs or outputs from ChatGPT Business, ChatGPT Enterprise, ChatGPT Edu or its API to improve its models by default.38 Its enterprise privacy page states, "We do not train on your business data, and our models don't learn from your usage."39 Other major AI vendors draw similar lines between consumer and commercial terms, but the details differ and change, so read the current terms of each tool.
| Question | Typical consumer account | Typical business or enterprise account |
|---|---|---|
| Are prompts used to train models? | Often yes by default, with an opt-out setting each user must find | Usually no by default, stated in the contract |
| Who controls the account? | The individual employee | The firm, with central administration and the ability to remove users |
| Data retention | Set by the vendor's consumer policy | Often configurable; may include shorter retention |
| Security commitments | General privacy policy | Contract terms, often with SOC 2 reports and data processing terms |
| Can the firm see what was entered? | No | Usually, through admin and audit tools |
The table describes patterns, not any vendor's current terms. The lesson for a firm is that the decision belongs at the firm level, through a business agreement the firm has read, rather than at the level of an individual employee's free account. Opinion 512's informed consent requirement applies to self-learning tools; a business tool whose contract bars training on the firm's data and keeps each customer's data separate may fall outside that category, but the firm still has to read the terms to know.
Hallucinations and court orders
The accuracy problem is not hypothetical. In Mata v. Avianca, a personal injury case in the Southern District of New York, the plaintiff's lawyers filed an affirmation opposing a motion to dismiss that cited court decisions that did not exist; the citations had come from ChatGPT. On June 22, 2023, Judge P. Kevin Castel imposed a $5,000 penalty, jointly on two lawyers and their firm, in an opinion and order on sanctions.40 As the case drew attention in spring 2023, some judges began issuing orders about AI. One widely reported example: on May 30, 2023, Judge Brantley Starr of the Northern District of Texas required attorneys appearing before him to file a certificate stating either that no part of a filing was drafted by generative AI or that any AI-drafted language was checked for accuracy by a person.41 Orders like this vary by judge and court and change over time. Before filing, check the local rules and the assigned judge's standing orders and practice requirements in each court; this lesson does not list them because they change too often to keep current.
Rules for a firm AI policy
A short written AI policy does more than a long one nobody reads. The common elements are:
- A list of approved tools and approved uses, owned by a named person, with everything else prohibited for client work.
- No client information in consumer accounts, ever. Personal accounts are not firm systems.
- For each approved tool, a record of the terms the firm reviewed: training on inputs, retention, location, subcontractors and security reports.
- A rule on when client consent is needed (self-learning tools, or whenever a client has asked not to have AI used) and a standard, specific consent form that explains the tool and the risk, not a sentence buried in the engagement letter.
- Minimum necessary input: remove names, account numbers and identifiers when the task does not need them.
- Verification: a person checks every citation, quotation, number and factual claim before anything leaves the firm.
- Recording and billing rules consistent with Opinion 512.
- Training for every lawyer and staff member, repeated when tools change, and an easy way to ask whether a new tool is allowed.
Retention, return and destruction
Data the firm no longer holds cannot be stolen from it. ABA Formal Opinion 483, on lawyers' duties after a breach, notes that old files kept under record-retention rules still contain former-client information protected by Rule 1.9(c), and it encourages data minimization.42 The general method for retention schedules and defensible deletion is in Records Retention, Legal Holds and Workplace Privacy. Here are the rules specific to professional firms.
Idaho Rule 1.16A: client files
Idaho has a rule of professional conduct devoted to client files, Rule 1.16A, with no numbered counterpart in the ABA Model Rules. It requires a lawyer to make the client's file available "within a reasonable time after the client's request," defines the file to include materials "regardless of whether the materials are in physical or electronic form," and lists what is in it: everything the client provided, all correspondence, pleadings and court records, discovery and investigative materials (including "medical records"), legal opinions, third-party records the client paid for, and copies of notes and documents prepared in the representation.11 The rule lets a lawyer withhold some items, including "electronic documents or information such as metadata that would be unreasonably burdensome or expensive for the lawyer to identify, locate, and produce in a readable or accessible format."11
The comments matter for data handling. Comment [2] says lawyers "should address the disposition of client files in a written fee agreement or engagement letter" or, failing that, in the final communication at the end of the matter. Comment [4] allows a lawyer to "maintain a client's file in electronic form," but requires "reasonable efforts to store such electronic files in a form that can be read with available technology for the period during which the file must be retained," and says an original whose form is important "should not be destroyed without the client's authorization." Comment [5] says the rule does not override court orders, discovery rules, subpoenas or "the law of spoliation and obstruction of justice," and that where several retention periods apply, the lawyer should keep the document for "the longest applicable period."11
Rule 1.16A does not set a fixed number of years for keeping a closed file. Idaho Rule 1.16(d) adds that at the end of a representation a lawyer must surrender "papers and property to which the client is entitled," and "may retain papers relating to the client to the extent permitted by other law."11 The one firm-wide number in the Idaho rules is for trust account records: Rule 1.15(a) requires complete records of trust funds and other property to be "preserved for a period of five years after termination of the representation."43 Trust accounts are the subject of lesson 3, Trust Accounts and Client Money.
Accounting and tax firm records
Idaho's accountancy rules (IDAPA 24.30.01) require a licensee to return client records on request "whether the engagement has been terminated or the licensee has been paid for services rendered," including copies of working papers to the extent they contain records that ordinarily form part of the client's books, in the medium requested if it exists in that medium.37 No general workpaper retention period appears in the current Idaho rules; the only explicit period found is for peer review documents.37 For tax firms covered by the FTC Safeguards Rule, 16 CFR 314.4(c)(6) requires secure disposal of customer information "no later than two years after the last date the information is used," unless it is needed for business operations or another legitimate purpose or the law requires keeping it, plus a periodic review of the data retention policy.20 IRS Publication 5708, the IRS's template for a written information security plan, includes a sample record retention policy as Attachment A.44
Secure disposal
Disposal is where many firms lose data without being hacked at all: a box of files in a recycling bin, a copier returned at lease end with its drive intact, a retired laptop sold online. Two federal sources set the practical standard.
The FTC's Disposal Rule, 16 CFR 682.3, applies to "any person who maintains or otherwise possesses consumer information for a business purpose," meaning information derived from consumer reports, which includes background checks a firm runs on employees or tenant and credit reports gathered for a client matter. It requires "reasonable measures to protect against unauthorized access to or use of the information in connection with its disposal," and gives examples: burning, pulverizing or shredding papers "so that the information cannot practicably be read or reconstructed"; destroying or erasing electronic media to the same standard; and, after due diligence, contracting with a record destruction business and monitoring its compliance.45 The rule's reach is limited to consumer report information, but its examples are a sensible floor for all client data.
For electronic media, the reference most firms and disposal vendors use is NIST Special Publication 800-88, Guidelines for Media Sanitization. Revision 2 was published September 26, 2025, replacing Revision 1 from December 2014.46 It helps an organization choose a sanitization method that matches the sensitivity of the data and the type of media, and it addresses modern techniques such as cryptographic erase. Ask any disposal vendor which method it uses, whether it follows SP 800-88, and for a certificate listing each device by serial number.
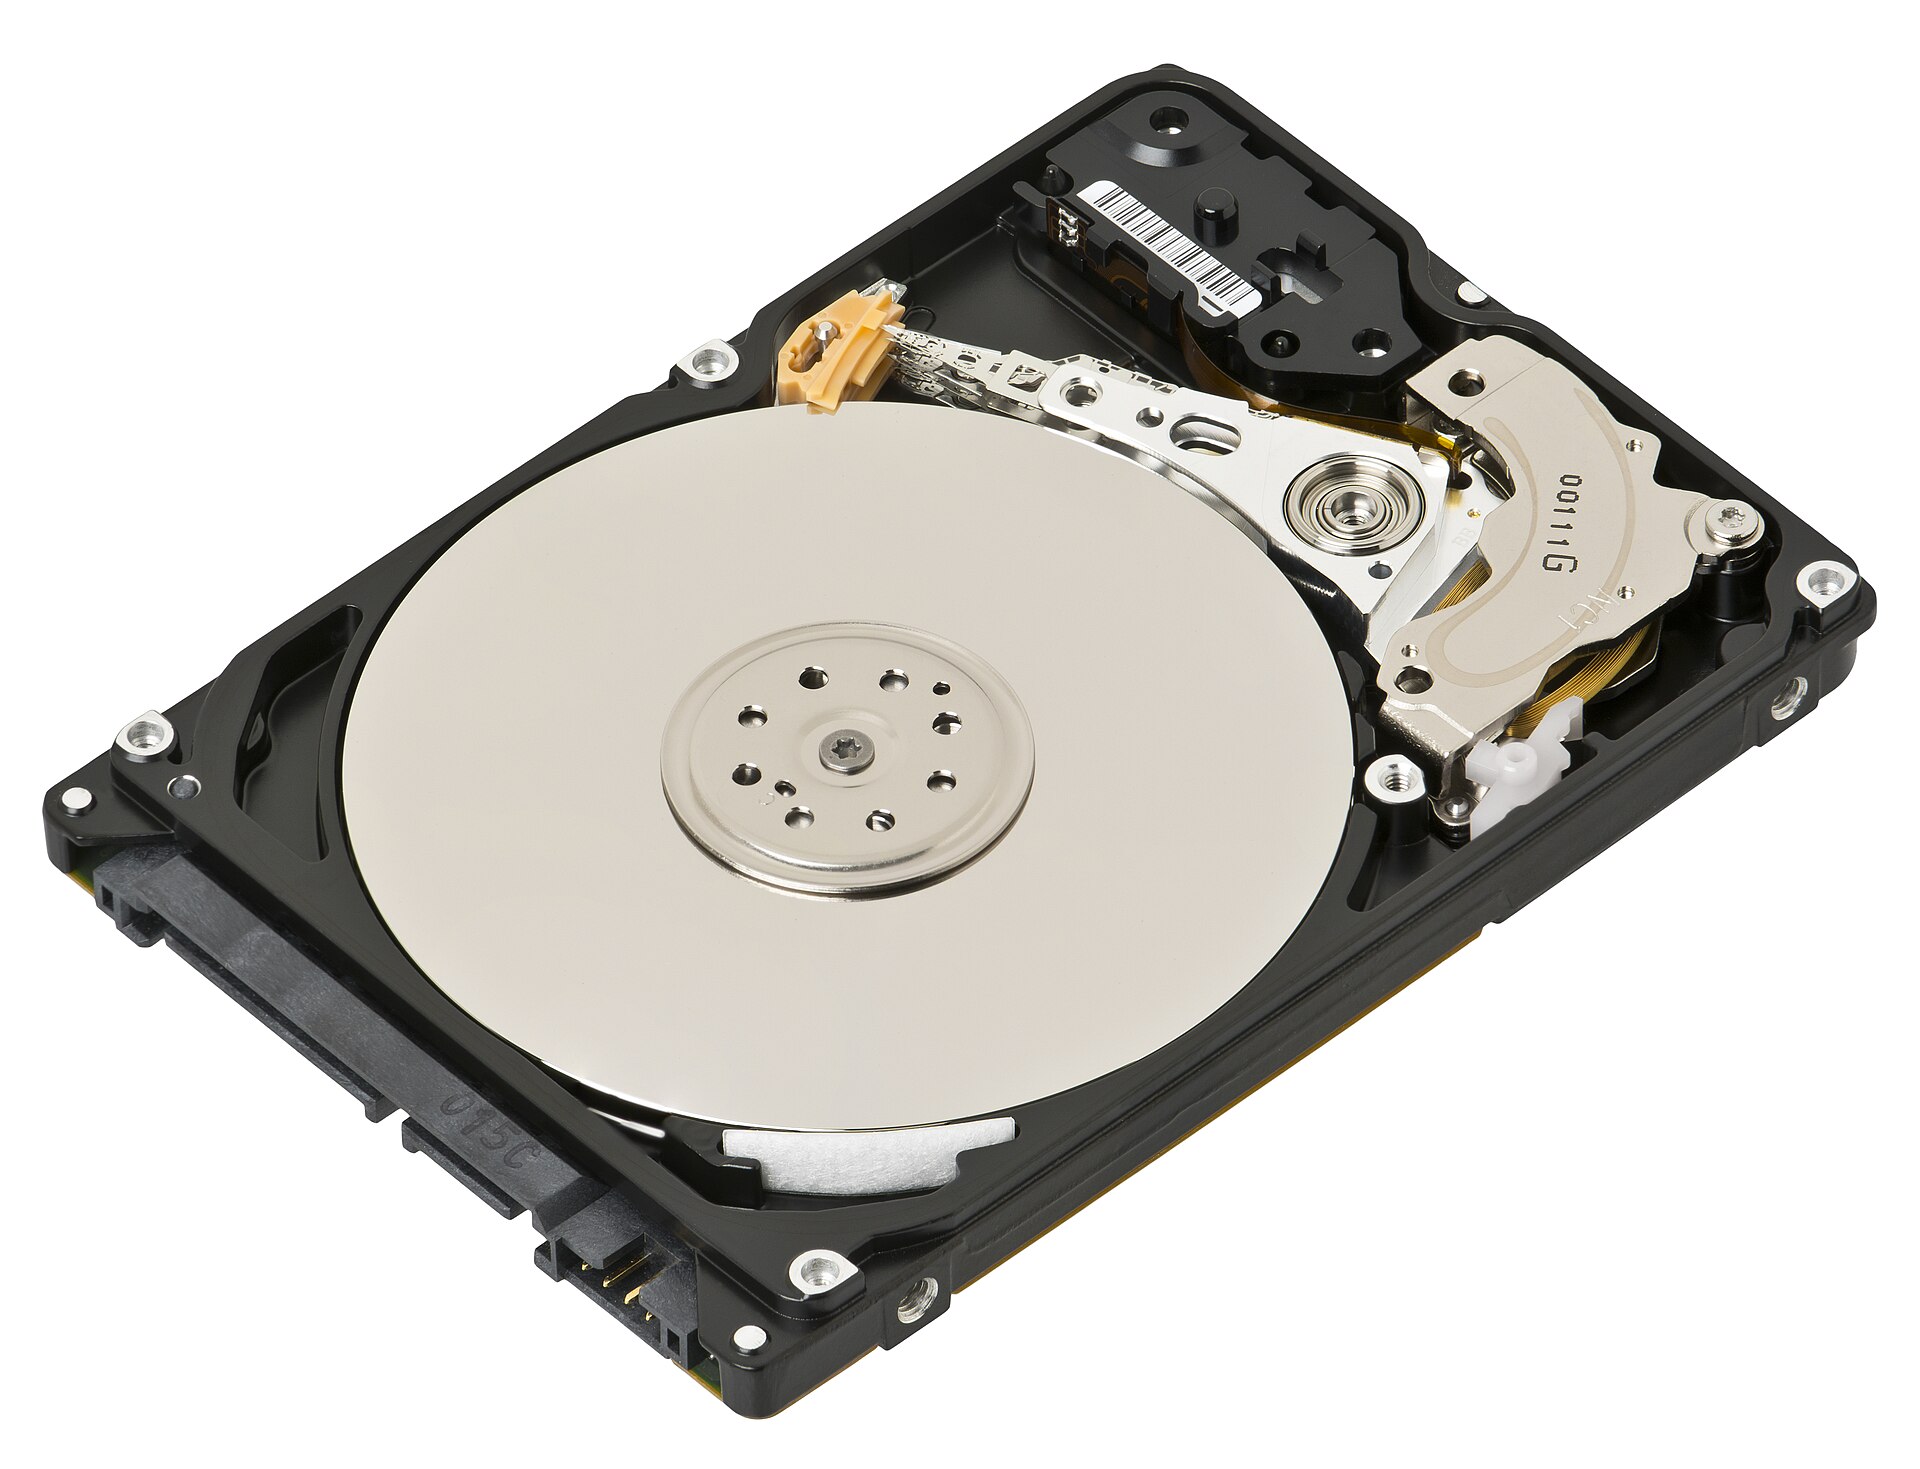

Do not forget the devices that do not look like computers. Multifunction copiers and scanners often store images of every page they process. Phones and tablets hold texts and email. Network storage boxes and old servers in a closet hold years of files. Encrypting devices when they are put into service makes disposal easier, because destroying the key makes the data unreadable. Paper still needs a locked shred bin or a bonded shredding service, and the shredding service is a vendor whose contract and performance should be checked like any other. Idaho's breach statute does not include a general business disposal requirement, and no other general Idaho disposal statute was found, so the professional rules, the FTC rules and client contracts are the main sources of the duty for most Idaho firms.18
Real incidents and what they teach
Most firm breaches never become public cases. The ones that do teach the same few points. Facts below come from government records where available; where only news reports exist, the lesson says so.
MOVEit, 2023: a vendor tool becomes the breach
As described above, the Cl0p group's mass exploitation of the MOVEit Transfer file transfer product over Memorial Day weekend 2023 reached thousands of organizations. According to press reports citing RollOnFriday, large law firms including Kirkland & Ellis, K&L Gates and Proskauer Rose were among them; Law.com reported a class action against Kirkland in June 2024.31 The point: a tool bought to move files securely became the path for taking them. Vendor tools belong in the data map and in the firm's patch and incident plans.
Orrick, 2023: an $8 million settlement
Orrick, Herrington & Sutcliffe suffered a breach in 2023 that exposed names, addresses, birth dates and Social Security numbers of people whose data the firm held for clients, according to the plaintiffs. The firm first reported about 153,000 people affected; more than 638,000 eventually received notices. The ABA Journal reported on November 12, 2024 that Judge Susan Illston of the Northern District of California gave final approval to an $8 million class settlement.47 These facts come from press reports; the case caption and docket were not read for this lesson. The point: the people suing were mostly not Orrick's clients but individuals whose data Orrick held for clients, and the count of affected people grew more than fourfold after the first estimate.
Bryan Cave Leighton Paisner and Mondelez, 2023 breach
The ABA Journal reported on October 11, 2024 that Bryan Cave Leighton Paisner and its client Mondelez Global agreed to pay $750,000 to settle suits by about 53,000 current and former Mondelez employees whose data was exposed in a hack of the law firm's network, with up to $250,000 for class counsel; the judge was Jorge L. Alonso.48 These facts are press-reported. The point: a client's employees can sue both the client and its law firm, and the client may end up paying for its firm's breach. That is why corporate clients now send security questionnaires.
Grubman Shire Meiselas & Sacks, 2020: ransomware and extortion
In May 2020 the REvil ransomware group hit the New York entertainment law firm Grubman Shire Meiselas & Sacks, claimed to have taken 756 gigabytes of data about celebrity clients, and raised its demand from $21 million to $42 million. The firm said it would not pay, telling Rolling Stone that "negotiating with or paying ransom to terrorists is a violation of federal criminal law," and that it was working with the FBI.49 Whether any payment was later made is not confirmed. The point: modern ransomware is also data theft and public extortion, so backups alone do not solve it; the stolen files are what the criminals use to pressure the victim. Data the firm no longer needed would not have been in the 756 gigabytes.
Heidell, Pittoni, Murphy & Bach: a regulator steps in
The New York Attorney General's $200,000 settlement in March 2023, described in the HIPAA section, is the clearest government record of a law firm's data failures: an unpatched email server months after the fix was released, no encryption of stored data, and too much old data kept.29 The required fixes read like a checklist for any firm: a written security program, encryption, central logging kept at least a year, patch management, penetration testing and deletion of data no longer needed.
Sample policy
The sample below pulls the lesson together for a small or mid-sized law or accounting firm. It is deliberately short. Fill in the brackets, delete what does not fit, and connect it to the firm's written information security program.
Sample only. Adapt it to your firm's risks, systems and laws, have qualified people review it, and do not treat it as a substitute for a risk assessment.
Follows: Idaho Rules of Professional Conduct 1.1, 1.6(c), 1.15(a), 1.16A and 5.3 (current as of March 9, 2026); ABA Formal Opinions 477R, 483 and 512; FRCP 26 and 37(e) and FRE 502; I.R.C.P. 26 and 37(e); 45 CFR 164.512(e)(1)(v); 16 CFR 682.3 and 314.4(c)(6); NIST SP 800-88 Rev. 2.
Client data handling, legal hold and secure disposal policy (sample)
1. Purpose and scope. This policy covers all information relating to the representation of [Firm Name]'s clients, prospective clients and former clients, in any form, wherever it is stored, including firm systems, approved cloud services, vendors' systems, mobile devices and paper. It applies to all partners, employees, contractors and temporary staff.
2. Owner. [Name, title] is responsible for this policy, for the client data map and for the approved systems list. Questions go to [contact].
3. Data map. The firm keeps a written map of every system, vendor and location that holds client data, with the owner, who has access, whether multi-factor sign-in and encryption are on, and how long data is kept. The map is updated [annually] and whenever the firm adds or replaces a system or vendor.
4. Classification. Each matter is assigned the highest tier of data it contains: Restricted (protected health information received under HIPAA or a qualified protective order; sealed or attorneys' eyes only material; trade secrets and pending transaction information), Confidential Regulated (Social Security, driver's license and financial account numbers; tax return information; client medical records), Confidential Privileged, or Confidential Ordinary. The handling rules for each tier are in Appendix [A]. Client instructions requiring extra security are recorded on the matter.
5. Approved systems. Client data may be stored and sent only through systems on the approved list in Appendix [B]. Personal email, personal cloud accounts, personal messaging apps and consumer AI accounts may not be used for client data. Firm email to clients containing Restricted or Confidential Regulated data is sent through [secure portal or encrypted email].
6. Vendors. No vendor receives client data until [owner] has completed the due diligence checklist in Appendix [C], reviewed the vendor's security report or certification where available, and confirmed contract terms on confidentiality, encryption, breach notice within [number] [hours/days], subcontractors, data location, no use of firm data to train AI models, return and deletion at termination, and (where health information is involved) a business associate agreement. Vendors are reviewed again at renewal.
7. Generative AI. Only tools on the approved list may be used with client information, under the firm's business agreement. No client information may be entered into a tool that may train on or reuse it unless the client has given specific informed consent on the firm's form. A person verifies every citation, quotation, number and factual statement produced by an AI tool before it is used. Use of AI on a matter is recorded in [location].
8. Discovery and productions. For each litigated matter the responsible lawyer will consider, at the start of the case, a protective order with data security terms and, in federal court, an order under Federal Rule of Evidence 502(d), or in Idaho state court a stipulated clawback agreement. Productions are sent only by [approved encrypted method], logged with date, recipient, method and Bates range, and checked for privilege, hidden content and redactions by a second person before release. Review platform access is limited to named users with multi-factor sign-in and is reviewed [monthly].
9. Legal holds. When the firm reasonably anticipates litigation or an investigation involving the firm itself, or receives notice of a claim, investigation, disciplinary matter or Client Assistance Fund claim related to a client matter, [owner] will issue a written hold within [number] business days, identify custodians and systems (including phones, messaging apps and backups), apply technical holds where the system allows, suspend deletion for the affected data, and confirm receipt in writing. Holds are reviewed [quarterly] and released in writing when the matter ends. Before any system restore, device wipe or employee departure, IT checks the active hold list.
10. End of matter. At the close of each matter the responsible professional will: confirm no hold applies; return to the client the file materials the client is entitled to; return or destroy material as required by any protective order or qualified protective order, including all copies, and obtain certificates; close vendor platforms and remove access; and record the closing date and retention period.
11. Retention. Closed client files are kept for [number] years after the matter closes, or longer if required by law, court order, a hold or the client's written instruction, and trust account records for at least five years after the representation ends. Files kept electronically are stored encrypted in a format that can still be read for the whole retention period. Originals whose form is important are not destroyed without the client's authorization.
12. Secure disposal. At the end of the retention period, paper is shredded or pulped through [locked bins and a vetted shredding vendor]; electronic media and devices, including copier and scanner drives and phones, are sanitized or destroyed using methods consistent with NIST SP 800-88 by [IT provider or vendor], with a certificate listing each device. [Owner] keeps a destruction log of what was destroyed, when and by whom. Backups are allowed to expire on their normal schedule and are not restored to recover destroyed files except under a hold.
13. Training and enforcement. All personnel receive training on this policy at hire and [annually]. Violations are handled under [the firm's personnel policy]. Suspected loss or exposure of client data is reported immediately to [contact] under the firm's incident response plan.
Approved by [name, title] on [date]. Next review: [date].
Where this lesson links instead of repeating
- How to build an asset and data inventory and score risks: Risk Assessment and Data Mapping.
- Retention schedules, defensible deletion and the general hold process, with a sample hold notice: Records Retention, Legal Holds and Workplace Privacy.
- Vendor tiers, contract clauses and reading a SOC 2 report: Vendors, Contracts and Third-Party Risk.
- Settings for Microsoft 365, Google Workspace and shared links: Cloud, SaaS and Shared Files.
- Business associate agreements, cloud and AI vendors under HIPAA: Business Associates, Cloud and AI Vendors; HIPAA overview: Health Privacy: HIPAA and Beyond.
- Other lessons in this module: lesson 1 (the duties), lesson 3 (trust accounts), lesson 4 (GLBA Safeguards and IRS rules), lesson 5 (engagement letters, incident response and notice) and lesson 6 (business email compromise and wire fraud).
Common mistakes
- Leaving known patches unapplied on systems that hold client files. The New York Attorney General found that Heidell, Pittoni, Murphy & Bach's attacker used a Microsoft Exchange flaw even though "Patches for this vulnerability had been released by Microsoft several months earlier."29 An email server is a client data store.
- Keeping everything forever. The same settlement required data minimization and deletion, and Opinion 483 urges it.2942 Old closed files are pure risk once their retention period ends; the 756 gigabytes claimed in the Grubman Shire attack show how much an archive can hold.49
- Treating a vendor's tool as the vendor's problem. The MOVEit exposures reached law firms through a file transfer product.31 Rule 5.3 Comment [3] puts the duty to supervise such services on the firm.8
- Underestimating how many people are in the data. Orrick's count went from about 153,000 to more than 638,000.47 Firms often do not know how many individuals' records they hold for clients until a breach forces a count. The data map should include rough counts.
- Forgetting that a client's employees and customers can sue. The BCLP and Mondelez settlement resolved claims by the client's employees.48
- Producing without a clawback order. Relying on FRE 502(b)'s "reasonable steps" test after a mistake instead of getting a 502(d) order at the start, or, in Idaho state court, producing without any written clawback agreement when I.R.E. 510 treats voluntary disclosure of "any significant part" as a waiver.36
- Letting auto-delete run during a hold. Idaho Rule 37(e)'s safe harbor covers only "routine, good-faith" loss; federal Rule 37(e) asks whether "reasonable steps" were taken.524
- Using consumer AI accounts for client work. Consumer terms may allow training on inputs; Opinion 512 requires informed consent before client information goes into a self-learning tool.3810
- Filing AI output unchecked. Mata v. Avianca ended in a $5,000 sanction for citations to cases that did not exist.40
- Returning leased copiers and retiring laptops without sanitizing drives. The FTC Disposal Rule's examples and NIST SP 800-88 exist for this.4546
- Sharing client files by open links that never expire. An Idaho State Bar scam alert on April 22, 2024 warned that scammers were emailing Dropbox links with the goal of getting wire transfers for settlement funds.50 A firm that routinely sends clients open, permanent links teaches them to trust any link. Use expiring, access-controlled links, and tell clients how the firm will and will not share files.
Questions people ask
Is ordinary unencrypted email to clients allowed?
Generally yes, for ordinary matters. ABA Formal Opinion 477R says a lawyer "generally may transmit information relating to the representation of a client over the internet" if the lawyer has made reasonable efforts to prevent unauthorized access, but may need special precautions when required by agreement or law, "or when the nature of the information requires a higher degree of security."16 Idaho Rule 1.6 Comment [20] says the same in rule form: no special measures are required if the method "affords a reasonable expectation of privacy," but "Special circumstances, however, may warrant special precautions."1 Medical records, Social Security numbers, tax returns and deal documents are the usual special circumstances. Separately, ABA Formal Opinion 11-459 says lawyers should ordinarily warn clients about using an employer's email or device for communications with their lawyer when there is a significant risk the employer can read them.51
May a firm use a cloud service without telling clients?
Using ordinary cloud storage and software is generally treated as a supervised vendor relationship under Rule 5.3, and Idaho Comment [3] lists "using an Internet-based service to store client information" as an example without requiring client consent for it.8 ABA Opinion 08-451 calls for disclosure and consent when outsourced lawyers or nonlawyers will be receiving protected information to do legal or support work, which is a broader category than storage.34 CPAs should follow the AICPA interpretations: a confidentiality contract or the client's specific consent before disclosure to a service provider, and notice to the client of third-party providers except for administrative support such as storage and hosting.9 Many firms describe their main systems and vendors in the engagement letter, which costs little and avoids surprises.
Do we need client consent to use AI on a matter?
Under ABA Opinion 512, informed consent is required before entering client information into a self-learning tool that could expose it, and a general clause in the engagement letter does not count.10 For a business tool whose contract bars training on and sharing of the firm's data, consent may not be required for that reason, but other duties still apply, and some clients forbid AI use in the terms they set for the firms they hire. Tax preparers should check whether the use is a disclosure that needs 7216 consent.19
How long must we keep a closed file in Idaho?
The Idaho rules set no general number of years for a lawyer's closed client file. Rule 1.15(a) requires trust account records for five years after the representation ends, and Rule 1.16A(g) forbids destroying a file while a related claim, investigation, disciplinary matter or Client Assistance Fund claim is pending or anticipated.4311 Comment [2] to Rule 1.16A tells lawyers to address file disposition in the fee agreement or engagement letter. Firms set their own period in light of malpractice limitations periods, client needs and other law, and write it down. For Idaho CPAs, no general workpaper retention period appears in IDAPA 24.30.01, though tax firms covered by the Safeguards Rule must dispose of customer information within two years of last use unless an exception applies.3720
What if the other side sends us something privileged by mistake?
Idaho Rule 4.4(b) requires the receiving lawyer to promptly notify the sender if the lawyer knows or reasonably should know a document or ESI was inadvertently sent.22 If the sender then makes a clawback claim, Rule 26(b)(5)(B) in both federal and Idaho court requires the receiving party to return, sequester or destroy the information and not use it until the claim is resolved.24 Whether privilege was waived is a separate question decided by the court under FRE 502 or, in state court, Idaho law.
Our small firm cannot afford an e-discovery vendor. What then?
Small cases often run on the firm's own tools: PDFs, a document management system, a shared drive. The same rules apply. Keep productions in a restricted folder for the matter, send them by an encrypted method, log what went out, scrub metadata and check redactions, and destroy copies at the end as any protective order requires. Proportionality in federal court and cost shifting under Idaho Rule 34(b) can also help keep the volume manageable.225
We do personal injury work. Are we a HIPAA business associate?
Usually not for that work. A firm representing an injured patient receives the records on the patient's behalf, not as a service to the hospital, so the business associate definition does not fit. The firm is a business associate when its client is the covered entity (a hospital, clinic, doctor's practice or health plan) and the legal or accounting services involve PHI from that client.28 Either way, Rule 1.6 protects the records, and records obtained under a qualified protective order must be returned or destroyed at the end of the case.7
Hard questions
Should Idaho adopt its own version of FRE 502(b) and (d)?
The case for: without a state rule, a privileged document produced by mistake in Idaho state court risks waiver under Idaho Rule of Evidence 510's "any significant part" language, and parties must rely on private agreements whose effect on third parties is uncertain.6 A court order with the reach of FRE 502(d) would let parties produce faster and cheaper, which matters most in high-volume ESI cases, and would bring state and federal practice in Idaho into line.3 The case against: Idaho's civil caseload is mostly smaller cases where volume rarely justifies the change; stipulated clawback agreements and protective orders already handle most problems; and broad non-waiver orders can encourage parties to skip careful privilege review and dump documents. What the evidence shows: no Idaho appellate decision on waiver by inadvertent ESI production was located for this lesson, so there is little Idaho data on how often the gap causes harm. The texts show the gap exists; whether it matters enough to change the rule is a policy judgment for the Idaho Supreme Court's rules process.
Should firms need client consent before any AI use on a matter?
The case for: clients cannot easily check how a firm's tools handle their data, terms of service change, and accuracy failures such as Mata v. Avianca harm the client first.40 A consent rule for all AI use would be simple to follow and would give clients a real choice. The case against: AI features are being built into word processors, email, research services and document systems the firm already uses; a consent rule for every AI feature would make consent forms meaningless boilerplate, which Opinion 512 itself rejects. Opinion 512 instead ties consent to the risk: self-learning tools that may expose client information.10 What the evidence shows: the ABA chose a risk-based approach in July 2024, and Idaho has not addressed the question. Vendor terms differ sharply between consumer and business accounts, which supports focusing on the tool's terms rather than on AI as a category.38
Should standard protective orders carry mandatory data security terms?
The case for: a protective order that limits who may see a trade secret but says nothing about where it is stored or how fast a breach must be reported leaves the producing party with little remedy when the receiving firm is hacked. The breaches at firms of every size described in this lesson show that receiving firms are real risks.4729 Standard terms (multi-factor sign-in, encryption, breach notice, certified destruction) would set a floor. The case against: fixed technical terms can be out of date within a few years, small firms and individual litigants may not be able to meet them, and fights over security terms add cost and delay to discovery. What the evidence shows: HIPAA's qualified protective order rule already requires return or destruction of all copies for health information, showing that a minimal, technology-neutral term can be standard.7 Whether courts should go further is unsettled, and practice varies by judge.
Is keeping old client files a service to clients or a liability?
The case for keeping: clients lose their own copies, old estate planning and real estate files answer questions decades later, and a firm defending a malpractice claim needs its file. Idaho Rule 1.16A Comment [4] cautions against destroying originals whose form matters without client authorization.11 The case for destroying on schedule: every closed file is data that can be stolen, and the costs of a breach fall partly on people who were never the firm's clients. The New York Attorney General required data deletion as a remedy, and Opinion 483 points the same way.2942 What the evidence shows: breach cases show the cost of keeping too much; no comparable public record shows harm from destroying files on a disclosed schedule after the client was told and given a chance to take the file. A written schedule, disclosed in the engagement letter and carried out with a destruction log, satisfies both concerns better than either extreme.
For reporters and advocates
Court dockets. Class actions over law firm breaches are filed in federal and state courts and name the firm. Search PACER and state court systems for the firm's name with terms such as "data breach" or "negligence." Settlement papers often state the number of people notified, the categories of data and the security changes the firm agreed to make. The Orrick and BCLP settlements are examples reported by the ABA Journal.4748 In ordinary lawsuits, protective orders and sealing motions on the docket show what each side treated as confidential, and disputes over lost ESI under Rule 37(e) show up as sanctions motions.
State attorney general breach notices. Some states post copies of breach notice letters businesses send to residents, and law and accounting firms appear on those lists. Idaho does not: under Idaho Code 28-51-105, only public agencies must notify the Idaho Attorney General, within 24 hours; private firms notify affected residents but not the Attorney General.18 For Idaho residents affected by a firm breach, the letter itself, other states' posted lists and court filings are the main records.
Regulator actions. The New York Attorney General's Heidell, Pittoni settlement is a model of what an enforcement record can show: dates, the vulnerability, the number of people and the required fixes.29 Search attorney general press releases and the HHS breach portal (for firms acting as business associates) by firm name.
Bar discipline records. Search the Idaho State Bar website and Idaho Supreme Court opinions for discipline records. No Idaho discipline case on client data loss was located in the research for this module, and the absence of a found case is not proof none exists. Ask the Bar how many grievances it has received about lost or exposed client files, and whether it has considered technology guidance; its last formal ethics opinion series largely ended in the 1990s.36
Public agencies as clients. Counties, cities, school districts and state agencies hire law firms and e-discovery vendors. Under the Idaho Public Records Act, ask for engagement letters and vendor contracts (including data security and destruction terms), invoices showing review platform hosting charges for closed cases, and any breach notices received from firms or vendors. Expect some redactions for security details.
Questions to ask a firm after a breach. When did the firm discover it, and when did it notify clients and individuals? Which systems were involved, and was a vendor tool part of it? Were stored files encrypted? How many people's data did the firm hold for clients, and why was it still there? Did the firm have a data retention schedule, and was it followed? Has the firm changed its practices since?
Idaho angle. Idaho's court rules differ from the federal rules on proportionality, lost ESI and privilege waiver, which makes state court discovery a real story when large data sets are involved.45 Idaho's own Rule 1.16A on client files is unusual and gives reporters a clear standard to ask about.11 The Idaho State Bar's scam alerts, including the April 22, 2024 warning about Dropbox links used to pursue settlement funds, are public and dated.50 IC3's state data on Idaho complaints and losses is covered in lesson 6.
Where to go next
- Idaho State Bar: Idaho Rules of Professional Conduct: The official Idaho rules page and full-text PDF, including Rules 1.6, 1.15, 1.16A and 5.3 with comments. Free. Check the current-as-of date before relying on a rule.
- ABA Formal Opinion 512 (PDF): The ABA's guidance on generative AI for lawyers and firms. Free. Read it before writing a firm AI policy or client consent form.
- NIST SP 800-88 Rev. 2, Guidelines for Media Sanitization: Federal guidance on wiping and destroying drives, phones and other media. Free. Give it to your IT provider or disposal vendor and ask which methods they use.
- The Sedona Principles, Third Edition (Sedona Conference Journal PDF): Widely cited commentary on e-discovery preservation and production. Free download. Useful for writing a firm's hold and production procedures.
- IRS Publication 5708, Creating a Written Information Security Plan: Free IRS template for tax and accounting practices, with a sample record retention policy. Useful for law firms too as a starting structure.
- FTC: Safeguards Rule, What Your Business Needs to Know: Free FTC guide for tax preparers and other covered financial institutions on encryption, vendor oversight and disposal. Read with lesson 4.
- 45 CFR 164.512 (Legal Information Institute): The HIPAA rule on disclosures in court proceedings, including qualified protective orders. Free. Useful for injury, malpractice and health care defense practices.
Still being checked (11 items)
These points could not be fully confirmed against a primary source when this lesson was written and fact checked in October 2026. The text above states each one as uncertain.
- Zubulake v. UBS Warburg LLC, 220 F.R.D. 212 (S.D.N.Y. 2003), is described from its widely cited holding; the opinion text was not read in full or quoted for this lesson.
- The Sedona Principles are described from publication details; the wording of Principle 6 is paraphrased from secondary descriptions, not read in the Journal text.
- The MOVEit law firm victims (Kirkland & Ellis, K&L Gates, Proskauer Rose) and the June 2024 Kirkland class action come from press reports, not court or company records.
- The Orrick ($8 million) and Bryan Cave Leighton Paisner and Mondelez ($750,000) settlement figures come from the ABA Journal; case captions and dockets were not read.
- The Grubman Shire facts come from Rolling Stone; whether any ransom was later paid is not confirmed.
- Judge Brantley Starr's 2023 AI certification requirement is reported from a press account; whether it remains in effect was not checked.
- The conclusion that Idaho has no evidence rule equivalent to FRE 502(b) or (d), and no Rule 26(f)-style conference in I.R.C.P. 26, comes from reading the rule texts, not from a court ruling.
- Descriptions of SOC 2 Type 1 and Type 2 reports and ISO/IEC 27001 certification reflect general professional practice; the paid standards were not read.
- AI vendor terms are quoted from OpenAI pages as read Oct. 28, 2026 and can change; the statement that other vendors draw similar consumer and business lines was not checked vendor by vendor.
- No Idaho discipline case or Idaho appellate decision on client data loss or inadvertent ESI production waiver was located; absence of a found case is not proof none exists.
- The 678 F. Supp. 3d 443 reporter citation for the Mata v. Avianca sanctions opinion is from secondary sources; the opinion itself was read at Justia.
Last verified October 28, 2026. General education, not legal, ethics, accounting or compliance advice; rule versions and dates are stated in the text, and the sources used are listed in the Notes and Sources below. Check the regulator's current text before relying on any point.
Notes
- Idaho State Bar, Idaho Rules of Professional Conduct, Full Text (rules current as of March 9, 2026), Rule 1.6(a) and (c) and Idaho Comments [19] and [20] (Idaho Comment [19] corresponds to ABA Model Rule 1.6 Comment [18]) (read Oct. 28, 2026). Read it online. ↩
- Fed. R. Civ. P. 26(b)(1), (b)(2)(B), (b)(5)(B), (c) and (f)(3), as amended effective December 1, 2015, with advisory committee notes, Legal Information Institute, Cornell Law School (read Oct. 28, 2026). Read it online. ↩
- Fed. R. Evid. 502(b) and (d), Legal Information Institute, Cornell Law School (read Oct. 28, 2026). Read it online. ↩
- Idaho R. Civ. P. 26(b)(1)(A) and (B), (b)(5)(B) and (c)(1) (adopted March 1, 2016, effective July 1, 2016), Idaho Supreme Court rules website (read Oct. 28, 2026). Read it online. ↩
- Idaho R. Civ. P. 37(e), "Failure to Provide Electronically Stored Information," and 37(f) (adopted March 1, 2016, effective July 1, 2016), Idaho Supreme Court (read Oct. 28, 2026). Read it online. ↩
- Idaho R. Evid. 510 (waiver of privilege by voluntary disclosure) and Idaho R. Evid. 502 (lawyer-client privilege, at https://isc.idaho.gov/rules-procedure/print/ire/502), both adopted March 26, 2018, effective July 1, 2018. The statement that Idaho has no rule equivalent to FRE 502(b) or (d) is drawn from reading these texts, not from a court ruling (read Oct. 28, 2026). Read it online. ↩
- 45 CFR 164.512(e)(1)(ii) to (vi), disclosures for judicial and administrative proceedings, including the definition of a qualified protective order in (e)(1)(v), Legal Information Institute (current eCFR text) (read Oct. 28, 2026). Read it online. ↩
- Idaho State Bar, Idaho Rules of Professional Conduct, Full Text (rules current as of March 9, 2026), Rule 5.3, "Responsibilities Regarding Nonlawyer Assistance," and Idaho Comments [2] and [3], identical in text to ABA Model Rule 5.3 and its comments (read Oct. 28, 2026). Read it online. ↩
- AICPA Code of Professional Conduct, ET 1.700.001 (Confidential Client Information Rule), ET 1.700.040 (Disclosing Information to a Third-Party Service Provider) and ET 1.150.040 (Use of a Third-Party Service Provider), effective December 15, 2014, updated through December 2023, as hosted by the Minnesota Society of CPAs (read Oct. 28, 2026). Read it online. ↩
- ABA Standing Committee on Ethics and Professional Responsibility, Formal Opinion 512, "Generative Artificial Intelligence Tools" (July 29, 2024). Described; short quotations only (read Oct. 28, 2026). Read it online. ↩
- Idaho State Bar, Idaho Rules of Professional Conduct, Full Text (rules current as of March 9, 2026), Rule 1.16(d) and Rule 1.16A, "Client Files," paragraphs (a) to (g) and Commentary [1] to [6]. Rule 1.16A has no numbered counterpart in the ABA Model Rules (read Oct. 28, 2026). Read it online. ↩
- U.S. Attorney's Office, Southern District of New York, "Manhattan U.S. Attorney Announces Arrest Of Macau Resident And Unsealing Of Charges Against Three Individuals For Insider Trading Based On Information Hacked From Prominent U.S. Law Firms," December 27, 2016; see also SEC press release 2016-280 (read Oct. 28, 2026). Read it online. ↩
- International Consortium of Investigative Journalists, "Explore the Panama Papers Key Figures" (read Oct. 28, 2026). Read it online. ↩
- John Simek, "2023 Cybersecurity TechReport," ABA Law Practice Division, December 18, 2023, based on the 2023 ABA Legal Technology Survey Report. No later ABA cybersecurity TechReport was found (read Oct. 28, 2026). Read it online. ↩
- Idaho State Bar, Idaho Rules of Professional Conduct, Full Text (rules current as of March 9, 2026), Rule 1.1 and Comment [8], identical in text to ABA Model Rule 1.1 Comment [8] (read Oct. 28, 2026). Read it online. ↩
- ABA Formal Opinion 477R, "Securing Communication of Protected Client Information" (May 11, 2017, revised May 22, 2017), including its seven numbered considerations (read Oct. 28, 2026). Read it online. ↩
- Idaho Code 9-203A, confidential communications with accountants, Idaho Legislature (read Oct. 28, 2026). Read it online. ↩
- Idaho Code 28-51-104 (definitions, including "personal information") and 28-51-105 (notice duties, including the duty of an entity that maintains data it does not own and the 24-hour notice to the Attorney General that applies only to agencies), Idaho Legislature. No general business disposal requirement appears in Title 28, Chapter 51 (read Oct. 28, 2026). Read it online. ↩
- 26 U.S.C. 7216(a); 26 CFR 301.7216-2(d) and 301.7216-3(a) (consent requirements, including prior consent for disclosure to a preparer outside the United States), Legal Information Institute (read Oct. 28, 2026). Read it online. ↩
- 16 CFR 314.2(h)(2)(viii) and 314.4(c)(3), (c)(6) and (f) (FTC Standards for Safeguarding Customer Information, as amended 86 FR 70272, December 9, 2021), Legal Information Institute. The exceptions to the two-year disposal requirement are summarized, not quoted (read Oct. 28, 2026). Read it online. ↩
- Fed. R. Civ. P. 34(b)(2)(E), Legal Information Institute (read Oct. 28, 2026). Read it online. ↩
- Idaho State Bar, Idaho Rules of Professional Conduct, Full Text (rules current as of March 9, 2026), Rule 4.4(b) and Idaho Comment [4] (metadata) (read Oct. 28, 2026). Read it online. ↩
- ABA Formal Opinion 06-442, "Review and Use of Metadata" (August 5, 2006) (read Oct. 28, 2026). Read it online. ↩
- Fed. R. Civ. P. 37(e), as amended effective December 1, 2015, Legal Information Institute (read Oct. 28, 2026). Read it online. ↩
- Idaho R. Civ. P. 34(b), including the cost provision for extraordinary steps to retrieve ESI (adopted March 1, 2016, effective July 1, 2016), Idaho Supreme Court (read Oct. 28, 2026). Read it online. ↩
- Zubulake v. UBS Warburg LLC, 220 F.R.D. 212 (S.D.N.Y. Oct. 22, 2003) (Scheindlin, J.) ("Zubulake IV"), copy posted by the Association of Corporate Counsel. The opinion is described, not quoted; the description follows the widely cited reading of its holding (read Oct. 28, 2026). Read it online. ↩
- ABA Formal Opinion 482, "Ethical Obligations Related to Disasters" (September 19, 2018) (read Oct. 28, 2026). Read it online. ↩
- 45 CFR 160.103, definition of "business associate," paragraph (1)(ii), Legal Information Institute (read Oct. 28, 2026). Read it online. ↩
- New York State Attorney General, "Attorney General James Secures $200,000 from Law Firm for Failing to Protect New Yorkers' Personal and Health Information," March 27, 2023 (Heidell, Pittoni, Murphy & Bach LLP) (read Oct. 28, 2026). Read it online. ↩
- The Sedona Conference, "The Sedona Principles, Third Edition: Best Practices, Recommendations and Principles for Addressing Electronic Document Production," The Sedona Conference Journal, Vol. 19, No. 1 (2018); a copy is also posted by the U.S. District Court for the Eastern District of Pennsylvania. Principle wording is paraphrased (read Oct. 28, 2026). Read it online. ↩
- MSSP Alert, "Cl0p Hackers Hit Three of the Biggest U.S. Law Firms in Large Ransomware Attack" (2023), citing RollOnFriday; class action against Kirkland & Ellis reported by Law.com, June 10, 2024. Press reports (read Oct. 28, 2026). Read it online. ↩
- ABA Formal Opinion 498, "Virtual Practice" (March 10, 2021) (read Oct. 28, 2026). Read it online. ↩
- AICPA, "2017 Trust Services Criteria (With Revised Points of Focus, 2022)," the criteria used in SOC 2 examinations, covering security, availability, processing integrity, confidentiality and privacy. Described, not reproduced (read Oct. 28, 2026). Read it online. ↩
- ABA Formal Opinion 08-451, "Lawyer's Obligations When Outsourcing Legal and Nonlegal Support Services" (August 5, 2008) (read Oct. 28, 2026). Read it online. ↩
- ABA Formal Opinion 95-398, "Access of Nonlawyers to a Lawyer's Data Base" (October 27, 1995) (read Oct. 28, 2026). Read it online. ↩
- Idaho State Bar, Formal Ethics Opinions list (opinions No. 1, 1944, to No. 136, 1999), and "Notice of Formal Ethics Opinion" (Opinion 137, September 18, 2024). No opinion on cloud computing, email encryption, metadata, AI or data breaches was found (read Oct. 28, 2026). Read it online. ↩
- IDAPA 24.30.01, Idaho Accountancy Rules, rules 002 (incorporation of AICPA standards), 201 (confidential client information), 202 (records) and 212 (peer review documents), Idaho Division of Occupational and Professional Licenses (read Oct. 28, 2026). Read it online. ↩
- OpenAI Help Center, "How your data is used to improve model performance." Vendor terms change; this note records the page as read (read Oct. 28, 2026). Read it online. ↩
- OpenAI, "Enterprise privacy at OpenAI" (no date shown on page) (read Oct. 28, 2026). Read it online. ↩
- Bloomberg Law, "Phony ChatGPT Brief Leads to $5,000 Fine for NY Lawyers," June 22, 2023, reporting Mata v. Avianca, Inc., No. 1:22-cv-01461 (S.D.N.Y. June 22, 2023) (Castel, J.), reported at 678 F. Supp. 3d 443. The Opinion and Order on Sanctions (ECF No. 54, $5,000 imposed jointly and severally on Peter LoDuca, Steven A. Schwartz and Levidow, Levidow & Oberman P.C.) was read at Justia, https://law.justia.com/cases/federal/district-courts/new-york/nysdce/1:2022cv01461/575368/54 (read Oct. 28, 2026). Read it online. ↩
- Eugene Volokh, "Federal Judge Requires All Lawyers to File Certificates Related to Use of Generative AI," The Volokh Conspiracy (Reason), May 30, 2023, reporting the requirement of Judge Brantley Starr, U.S. District Court for the Northern District of Texas. Press report; whether the requirement is still in effect was not checked (read Oct. 28, 2026). Read it online. ↩
- ABA Formal Opinion 483, "Lawyers' Obligations After an Electronic Data Breach or Cyberattack" (October 17, 2018), including its discussion of Rule 1.9(c) and data minimization (footnote 45) (read Oct. 28, 2026). Read it online. ↩
- Idaho State Bar, Idaho Rules of Professional Conduct, Full Text (rules current as of March 9, 2026), Rule 1.15(a) (five-year preservation of trust account records) and Rule 1.9(c) (former clients) (read Oct. 28, 2026). Read it online. ↩
- IRS Publication 5708 (Rev. 8-2024), "Creating a Written Information Security Plan for your Tax & Accounting Practice," Attachment A, Record Retention Policies (read Oct. 28, 2026). Read it online. ↩
- 16 CFR 682.3, Proper disposal of consumer information (FTC Disposal Rule, under the Fair Credit Reporting Act), paragraphs (a) and (b)(1) to (b)(3), Legal Information Institute (read Oct. 28, 2026). Read it online. ↩
- National Institute of Standards and Technology, Special Publication 800-88 Rev. 2, Guidelines for Media Sanitization, September 26, 2025, superseding Rev. 1 (December 17, 2014) (read Oct. 28, 2026). Read it online. ↩
- ABA Journal, "Judge gives final OK to $8M settlement in Orrick data breach," November 12, 2024. Press report; case caption and docket not read (read Oct. 28, 2026). Read it online. ↩
- ABA Journal, "BigLaw firm and client agree to settlement in data breach suit by client's employees," October 11, 2024. Press report (read Oct. 28, 2026). Read it online. ↩
- Rolling Stone, report on the REvil ransomware attack on Grubman Shire Meiselas & Sacks, May 2020. Press report; whether any ransom was later paid is not confirmed (read Oct. 28, 2026). Read it online. ↩
- Idaho State Bar, Scam Alert posts, including April 22, 2024 (Dropbox links used to pursue wire transfers of settlement funds) (read Oct. 28, 2026). Read it online. ↩
- ABA Formal Opinion 11-459, "Duty to Protect the Confidentiality of E-mail Communications with One's Client" (August 4, 2011), headnote read in a copy hosted by Hinshaw & Culbertson (read Oct. 28, 2026). Read it online. ↩
Check yourself
1. What does Idaho Rule of Professional Conduct 1.6(c) require of a lawyer?
Idaho Rule 1.6(c), current as of March 9, 2026, requires reasonable efforts to prevent inadvertent or unauthorized disclosure of, or unauthorized access to, client information. It does not mandate specific technology, and the 24-hour Attorney General notice in Idaho Code 28-51-105 applies only to public agencies.
2. What does an order under Federal Rule of Evidence 502(d) do?
FRE 502(d) allows a federal court to order that privilege or protection is not waived by disclosure connected with the litigation before it, and the disclosure is then also not a waiver in any other federal or state proceeding.
3. How does Idaho Rule of Civil Procedure 26(b)(1) differ from the federal rule as amended in 2015?
I.R.C.P. 26(b)(1)(A), adopted 2016, keeps the "reasonably calculated" phrase that the 2015 federal amendment removed, and its text does not contain the federal proportionality factors.
4. What does Idaho Rule of Civil Procedure 37(e) say about lost electronically stored information?
I.R.C.P. 37(e) keeps the older federal-style safe harbor for ESI lost through routine, good-faith operation of a system; Idaho has not adopted the 2015 federal Rule 37(e) framework.
5. Under 45 CFR 164.512(e)(1)(v), a HIPAA qualified protective order must do what?
45 CFR 164.512(e)(1)(v) defines a qualified protective order as one that limits use to the litigation and requires return to the covered entity or destruction of the PHI, including all copies made, at the end of the proceeding.
6. When is a law or accounting firm usually a HIPAA business associate?
The definition of business associate in 45 CFR 160.103 includes persons providing legal, accounting, consulting and similar services to a covered entity where the service involves disclosure of PHI from that entity.
7. According to ABA Formal Opinion 512 (July 29, 2024), what is needed before entering client information into a self-learning generative AI tool?
Opinion 512 says informed consent is required for self-learning tools that may expose client information and that boilerplate engagement letter provisions purporting to authorize GAI use are not sufficient.
8. Under Idaho Rule 1.16A(g), when may a lawyer NOT destroy a client's file?
Idaho Rule 1.16A(g), current as of March 9, 2026, bars destroying a client's file in those circumstances.
9. How long must Idaho lawyers preserve complete trust account records under Rule 1.15(a)?
Idaho Rule 1.15(a) requires complete records of trust account funds and other property to be preserved for five years after termination of the representation. Idaho sets no general fixed period for the rest of the closed file.
10. Which is one of the examples of reasonable disposal measures in the FTC Disposal Rule, 16 CFR 682.3(b)?
16 CFR 682.3(b)(1) gives shredding, burning or pulverizing papers as an example; (b)(2) covers destroying or erasing electronic media so the information cannot practicably be read or reconstructed.
Terms in this lesson
- Electronically stored information (ESI)
- Any information kept in electronic form, such as email, documents, databases, texts and chat messages, that can be the subject of discovery.
- E-discovery
- Preserving, collecting, reviewing and producing electronically stored information in litigation or investigations.
- Data map
- A written inventory of where a firm's client data is stored, how it moves, who can reach it and how long it is kept.
- Proportionality
- The federal standard, added to FRCP 26(b)(1) in 2015, that discovery must be proportional to the needs of the case considering factors such as the amount in controversy and burden.
- Clawback
- The procedure under Rule 26(b)(5)(B) by which a party that produced privileged material by mistake gives notice and the receiving party must return, sequester or destroy it until the claim is resolved.
- FRE 502(d) order
- A federal court order that disclosure connected with the case does not waive privilege or work-product protection, in that case or any other federal or state proceeding.
- Legal hold
- An instruction to suspend routine deletion and preserve information that may be relevant to anticipated or pending litigation or an investigation.
- Protective order
- A court order limiting how discovery material may be used and who may see it, often with confidential and attorneys' eyes only tiers.
- Qualified protective order
- Under HIPAA, 45 CFR 164.512(e)(1)(v), an order or stipulation limiting use of health information to the case and requiring its return or destruction, including all copies, at the end.
- Business associate
- Under HIPAA, a person or firm, including a law or accounting firm, that performs services for a covered entity involving protected health information.
- Work product
- Documents and materials prepared in anticipation of litigation, protected from discovery under court rules, separate from attorney-client privilege.
- Metadata
- Data embedded in electronic files, such as authors, edit history, comments and hidden content, that may travel with a document when it is sent or produced.
- SOC 2 report
- An examination report by a CPA firm on a service organization's controls, based on the AICPA Trust Services Criteria; a Type 2 report tests whether controls worked over a period.
- Self-learning AI tool
- In ABA Formal Opinion 512's sense, a generative AI tool that may use inputs to train or improve itself, so that information entered could be exposed to others.
- Media sanitization
- Making data on storage media unrecoverable at a given level of effort, by clearing, purging or destroying the media, as described in NIST SP 800-88.
Sources
- Idaho Rules of Professional Conduct, Full Text (current as of March 9, 2026) (2026-03-09) checked 2026-10
- Federal Rules of Civil Procedure, Rule 26 (as amended Dec. 1, 2015) (2015-12-01) checked 2026-10
- Federal Rules of Civil Procedure, Rule 37 (as amended Dec. 1, 2015) (2015-12-01) checked 2026-10
- Federal Rule of Evidence 502 (2008-09-19) checked 2026-10
- Idaho Rules of Civil Procedure, Rule 26 (2016-07-01) checked 2026-10
- Idaho Rules of Civil Procedure, Rule 37 (2016-07-01) checked 2026-10
- Idaho Rules of Evidence, Rule 510 (waiver) (2018-07-01) checked 2026-10
- 45 CFR 164.512 (including qualified protective orders) (2026-10-28) checked 2026-10
- 45 CFR 160.103 (definition of business associate) (2026-10-28) checked 2026-10
- ABA Formal Opinion 512, Generative Artificial Intelligence Tools (2024-07-29) checked 2026-10
- ABA Formal Opinion 477R, Securing Communication of Protected Client Information (2017-05-22) checked 2026-10
- 16 CFR 682.3, FTC Disposal Rule (2026-10-28) checked 2026-10
- NIST SP 800-88 Rev. 2, Guidelines for Media Sanitization (2025-09-26) checked 2026-10
- New York Attorney General, $200,000 settlement with Heidell, Pittoni, Murphy & Bach LLP (2023-03-27) checked 2026-10